


AI Summary
Did a checker just tell you your domain has multiple SPF records? It’s worth fixing now, because it can break email authentication for every message you send.
A domain can only have 1 SPF record. With 2 or more, SPF fails with a permerror. The fix is to merge every TXT record starting with v=spf1 into one.
In this guide, I’ll show you how to find the duplicates and merge them correctly.
What Happens If You Have More than 1 SPF Record?
If your domain has 2 SPF records, SPF fails with a permerror. That stands for “permanent error.”
The SPF standard, RFC 7208, allows only 1 SPF record per domain. If a server finds more than one, the check returns permerror.
So the receiving server doesn’t pick one, and it doesn’t ignore both. It marks SPF as broken. That happens even for email from your real mail server.

What happens next is up to each receiving server. Some reject the email. Others accept it.
It also weakens DMARC. DMARC needs SPF or DKIM to pass and match your From domain. With a permerror, DMARC has to rely on DKIM alone.
If DKIM also fails, your DMARC policy determines what happens. That could mean spam or rejection.
You might not even know your records are broken. The good news is that merging them only takes a few minutes.
How to Fix Multiple SPF Records
First, we’ll confirm that you really have more than 1 SPF record. Then we’ll merge them in your DNS.
Check For Multiple SPF Records
You can check in a browser, from the command line, or inside WordPress. Pick whichever you’re comfortable with.
Option 1: Use an Online SPF Checker
I’ll use a free tool called MXToolbox. Type your domain into the Domain Name field and click SPF Record Lookup.

With more than 1 SPF record, MXToolbox flags a problem called SPF Multiple Records. Its result reads “More than one record found.”

In this example, 2 lines start with v=spf1. That’s what causes the error.
Option 2: Use the Command Line
You don’t need a website for this. On Windows, open Command Prompt from the Start menu. On a Mac, open Terminal from Applications » Utilities.
Type this command and press Enter. Swap example.com with your own domain.
nslookup -type=txt example.com
On macOS or Linux, dig gives a shorter answer:
dig TXT example.com +short
You’ll see every TXT record on your domain. Here’s a domain with duplicate SPF records:
"v=spf1 include:_spf.google.com ~all"
"v=spf1 include:mailgun.org ~all"
"google-site-verification=abc123"
Only count lines that start with v=spf1. Other TXT records, like site verification codes, are fine. This domain has 2 SPF lines, so it needs fixing.
When you’re done, just close the window.
Option 3: Use WP Mail SMTP’s Email Test
WP Mail SMTP can spot this for you. Go to WP Mail SMTP » Tools and open the Email Test tab. Then send a test email.
The plugin then runs a Domain Check on your From Email’s domain. It looks for the DNS records your mailer needs. Results only appear when there’s a problem.
With the Other SMTP mailer, it names this exact issue:
Action Needed: It looks like your domain (example.com) has multiple SPF records. Multiple SPF records aren't allowed and can cause your emails to be rejected.
With other mailers, it checks for the SPF record your provider needs. If it’s missing, you’ll see an Action Needed note about it. Either way, check for duplicates with Option 1 or 2.

Find Your SPF Records in Your DNS
Next, open the place where your DNS is managed. That’s usually one of these:
- Your domain registrar (where you bought your domain)
- Your web host, if your hosting and domain came as a package
- A DNS provider like Cloudflare, if your nameservers point there
Edit the records at whichever company your nameservers point to. Records anywhere else are ignored.
You may have been here before. It’s where you set up DMARC, SPF, and DKIM records for your email provider.
Example 1: SPF Records in Cloudflare
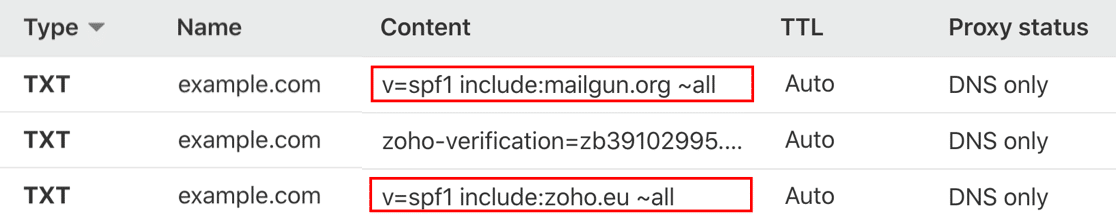
Log in to Cloudflare and select your domain. Then go to DNS » Records.

Look through the TXT rows for any that start with v=spf1.
Example 2: SPF Records in Bluehost
Log in to your Bluehost account. From the left-hand menu, click Domains.

From the list, click the domain you’d like to edit its records dropdown.

From the menu that pops out, scroll to the Manage Advanced DNS Records section.

Scroll down to your TXT records. Your SPF records are in this section.
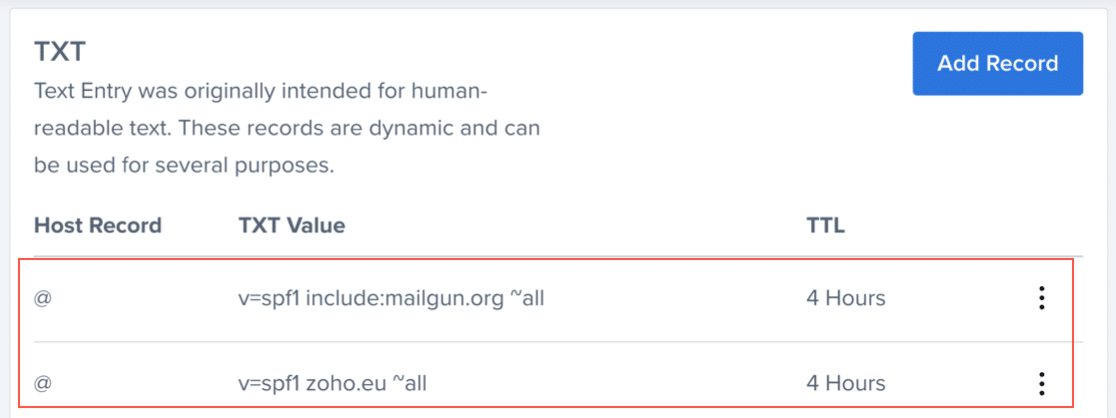
Most cPanel hosts use similar menus. If you can’t find your TXT records, ask your host’s support team.
Example 3: SPF Records in Namecheap
Log in to Namecheap and click Domain List. Then click Manage next to your domain.
Open the Advanced DNS tab. Your SPF records are the TXT Record rows starting with v=spf1. If you use Namecheap web hosting DNS, they’re in cPanel instead.
On another host, like GoDaddy, look for a DNS page in your domain settings.
How to Include Multiple SPF Records in 1 TXT Record
Now we’ll merge your SPF records into 1 TXT record. You’ll keep every sender and lose the error.
An SPF record has 3 parts:
- Version:
v=spf1at the very start. It appears once. - Allowed senders: the
include:,ip4:,ip6:,a, andmxparts. - Enforcement rule:
~allor-allat the very end. It also appears once.
To merge, keep 1 version tag and 1 enforcement rule. Put every allowed sender between them.

Merge Examples
Here are 2 common merges. Copy the exact values from your own records, not from here.
Google Workspace and Mailgun. These 2 records:
v=spf1 include:_spf.google.com ~all
v=spf1 include:mailgun.org ~all
Become 1 record:
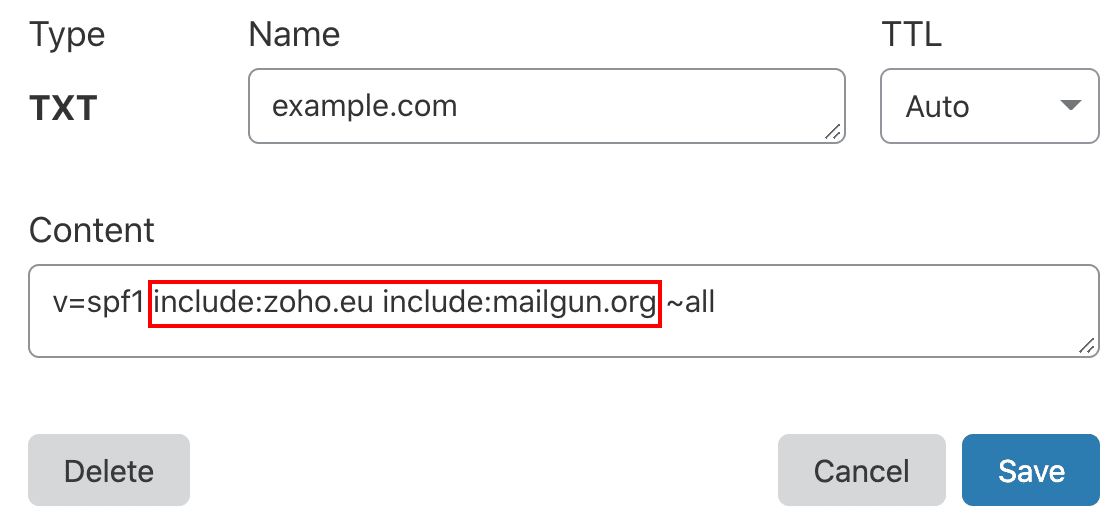
v=spf1 include:_spf.google.com include:mailgun.org ~all
Your own server, Microsoft 365, and Zoho Mail. An ip4: address merges the same way:
v=spf1 ip4:192.0.2.10 -all
v=spf1 include:spf.protection.outlook.com -all
v=spf1 include:zohomail.com -all
Merged:
v=spf1 ip4:192.0.2.10 include:spf.protection.outlook.com include:zohomail.com -all
Stopped using a service? Leave its include: out of the merged record.
These merges still break SPF:
- 2 version tags:
v=spf1 include:_spf.google.com ~all v=spf1 include:mailgun.org ~all - 2 enforcement rules:
v=spf1 include:_spf.google.com ~all include:mailgun.org -all - Typos:
include=instead ofinclude:, or a space after the colon
Records ending differently, like ~all and -all? Pick one. ~all is safer until you know every sender is listed.
Order matters a little. Servers read left to right and stop at the first match. Always put all last, because anything after it is ignored.
Edit the Record in Your DNS
I’ll use Cloudflare here, but the steps are similar on most hosts. Find your first SPF record and click Edit.
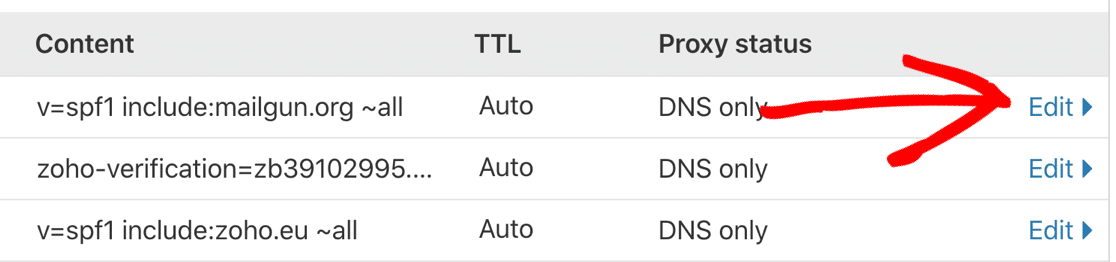
Copy the value into a blank text file so you don’t lose it. Then delete that record.
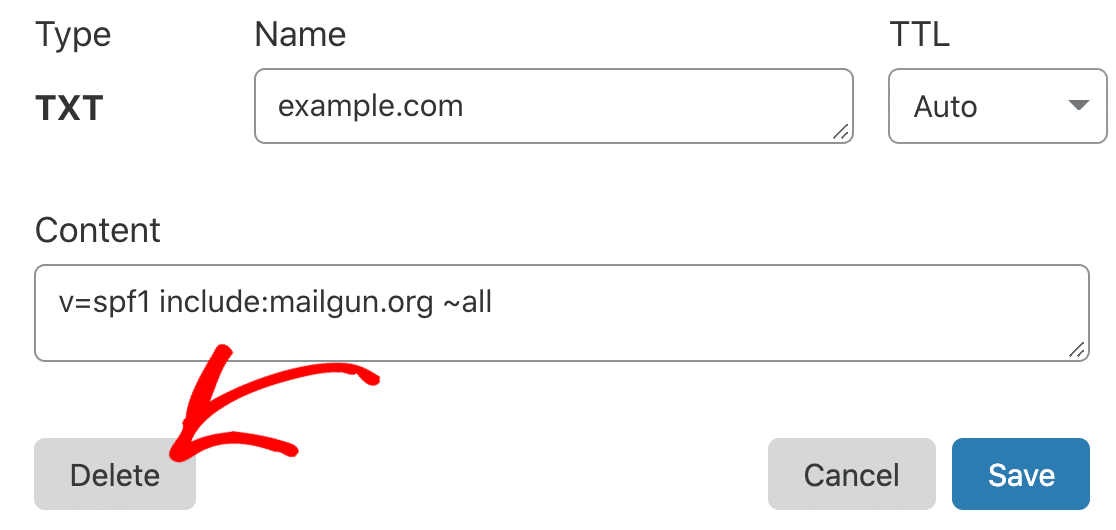
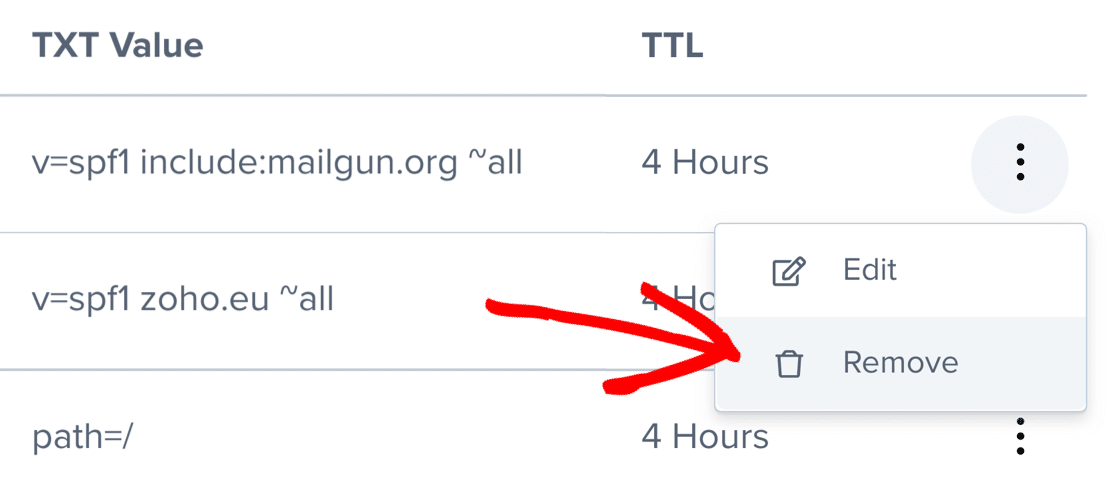
In Bluehost, you can delete the record with the 3-dot icon on the right. Then click Remove.
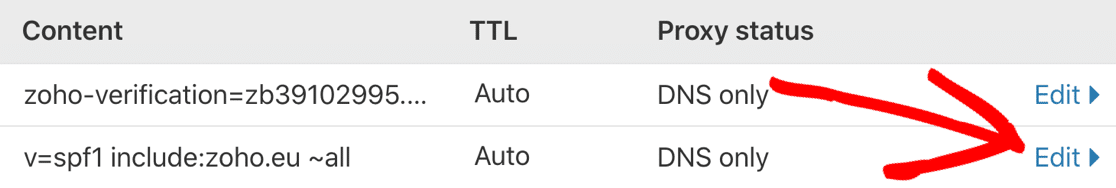
Back in Cloudflare, click Edit next to the second SPF record.
Replace its value with your merged record, all on 1 line. Then click Save.
Stay Under the 10 DNS Lookup Limit
A long merged record can hit a second limit. SPF allows at most 10 DNS lookups per check. Go over it, and you get a permerror again.
Each include:, a, mx, ptr, exists, and redirect= costs a lookup. ip4:, ip6:, and all are free.
Nested includes count too. For example, include:mailgun.org points to 2 more includes. One of those points to 2 more. So that one line uses 5 lookups.
Providers change their records, so count with a tool, not by hand. MXToolbox’s SPF check shows the total.

There’s a smaller limit for “void lookups,” too. A void lookup is a DNS lookup that comes back empty.
That’s often a service you stopped using. The standard allows only 2.
Over the limit? Try these in order:
- Remove includes for services you don’t use anymore.
- Move a sender, like a marketing tool, to a subdomain such as
news.example.com. Each subdomain gets its own record and its own 10 lookups. - Ask your provider if it offers a shorter SPF value.
SPF flattening swaps includes for raw IP addresses. It works, but you’ll need to update the record whenever a provider changes its IPs.
Also, each text string in a TXT record maxes out at 255 characters. Most DNS hosts split longer records for you.
Bulk-Sender Rules That Affect SPF
Google requires every sender to use SPF or DKIM, and to send over TLS.
At 5,000+ messages a day to Gmail, you need SPF, DKIM, and DMARC. Keep your spam rate in Google Postmaster Tools under 0.10% too.
Google said Gmail started “ramping up its enforcement” in November 2025. That can mean temporary or permanent rejections. Microsoft has had similar bulk-sender rules since May 2025.
Test Your Merged SPF Records
DNS changes can take up to 48 hours to spread. Cloudflare changes often show up in minutes.
After a while, check your domain in MXToolbox again. Or rerun the command from Option 2. You should see 1 v=spf1 line and a pass message.
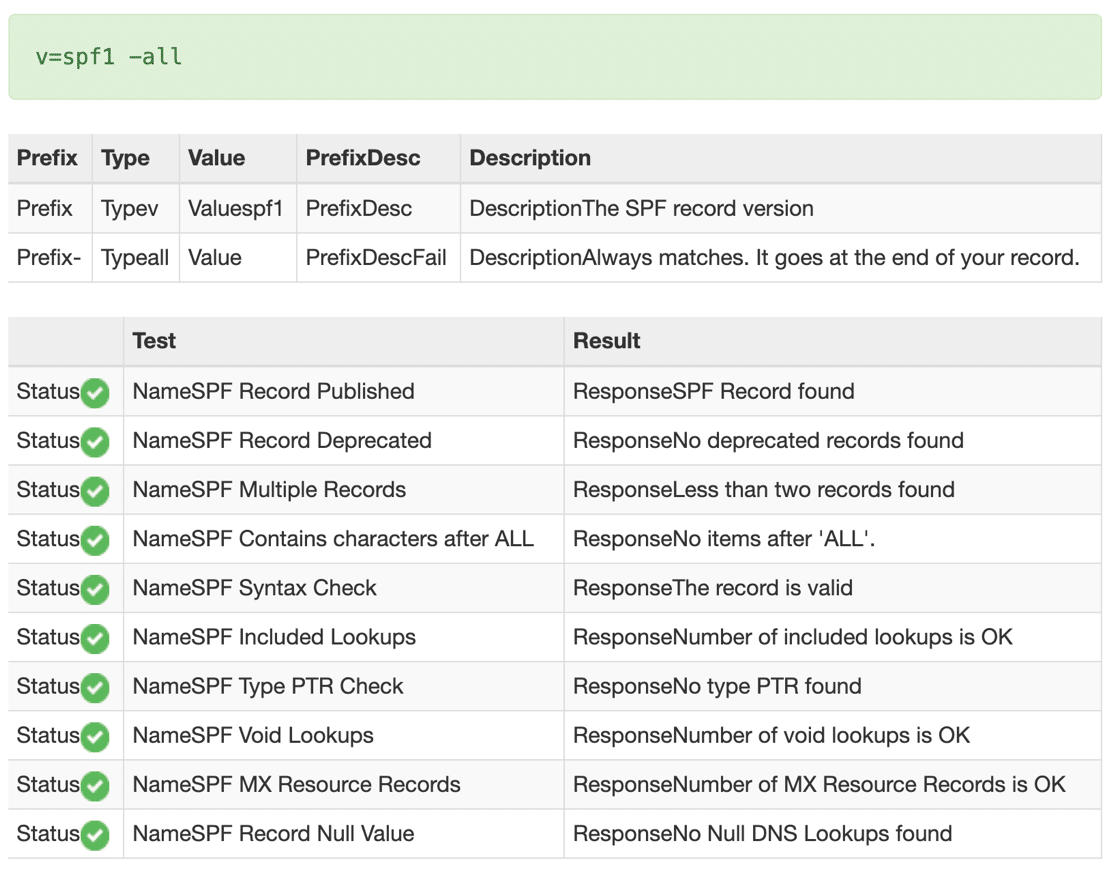
On WordPress, send another test from WP Mail SMTP » Tools » Email Test. No SPF warning means you’re set.
And that’s it! Your domain now has a single, valid SPF record.
What If I Still See an Error?
The Checker Still Shows 2 Records
Your old record may still be cached. Wait for its TTL (cache time) to run out, then check again.
Still there after a day? You may have edited the wrong DNS host. Edit the records where your nameservers point.
“Too Many DNS Lookups” or PermError
Your merged record needs more than 10 lookups once nested includes are counted. Follow the steps in the lookup-limit section above.
“Void Lookup Limit Exceeded”
One or more parts of your record point to a domain that no longer exists. That’s often an include:, a, or mx for an old service. Remove the ones you no longer use.
SPF Passes but DMARC Fails
SPF checks the hidden “return path” address, not the From address people see. Many providers use their own return path domain. Then SPF passes but doesn’t match your From domain.
In that case, DKIM has to carry DMARC. Make sure your provider’s DKIM record is set up.
Frequently Asked Questions
Let’s finish up with a little more background on SPF records.
What Does SPF Mean?
SPF stands for Sender Policy Framework. It’s defined in RFC 7208, which replaced the older RFC 4408.
What Does an SPF Record Do?
SPF helps stop domain spoofing. That’s when a spammer pretends to be you to send phishing emails.
A receiving server checks the sending server against your SPF record. If the check fails, the email may go to spam or get rejected.
How Many SPF Records Can I Have Per Domain?
You can have 1 SPF record per domain name. A second one causes a permerror, so merge them instead. Each subdomain that sends email gets its own single record.
Is SPF Required for WordPress Emails?
Usually, yes. Gmail requires SPF or DKIM from every sender, and both from bulk senders.
By default, WordPress doesn’t authenticate the emails it sends. An SMTP plugin like WP Mail SMTP sends through a real email provider instead.
Add the DNS records that provider asks for, and your mail can pass. Our guide on why Gmail blocks emails covers what happens when it doesn’t.
Is SPF Required for Every Mailer in WP Mail SMTP?
No. It depends on your mailer.
Some providers need an include: in your SPF record. Others handle SPF on their own domain or a subdomain.
Brevo’s setup asks for a Brevo code, DKIM, and DMARC, but no SPF change. SendLayer adds CNAME records on an sl subdomain instead.
To check yours, send a test from WP Mail SMTP » Tools » Email Test. If your mailer needs SPF and it’s missing, you’ll see a warning like this:
Action Needed: It doesn't look like the SPF record required by Google has been added to your domain. Please check out Google's SPF guide for details on how to add this record to your domain's DNS.The check is skipped for free addresses like gmail.com or outlook.com.
What Happens If I Have No SPF Records?
SPF returns “none.” That’s not a failure, but receiving servers get nothing to trust.
DMARC can still pass if DKIM passes and matches your From domain. But Gmail’s bulk rules need both, so set up both.
How Did I Wind Up With Multiple SPF Records?
Usually by accident. Here are the common causes:
- You use 2 services: For example, Brevo for WordPress emails with WP Mail SMTP, and another tool for newsletters. Each told you to “add an SPF record.”
- You switched providers: You added the new record but didn’t remove the old one.
- Your host added one: Some hosts create a default SPF record. Adding your own next to it makes 2.
If I Have Multiple SPF Records, Will My Test Email in WP Mail SMTP Still Work?
It might. Some customers have told us their test emails still arrive. That can happen because:
- Each server decides what to do with a
permerror. Some accept the email. - DKIM can still pass and satisfy DMARC.
- Your mailer may not use your domain’s SPF at all.
A delivered test doesn’t mean SPF is fine. Check the Domain Check results, and fix duplicates now.
Does SPF Apply to My Subdomains?
No. Unlike DMARC, SPF doesn’t cover subdomains automatically. Each subdomain that sends email needs its own SPF record.
What Does “Too Many DNS Lookups” Mean?
Your SPF record needs more than 10 DNS lookups, counting nested includes. Microsoft’s bounce messages call this “The message exceeded the hop count” or “The message required too many lookups.”
Remove unused includes, or move a sender to a subdomain. SPF flattening is another option, but it needs regular upkeep.
What Does -all vs ~all Mean?
They tell servers what to do with email from senders that aren’t listed.
-all(hard fail): those senders aren’t allowed. Servers often reject the email.~all(soft fail): those senders probably aren’t allowed. The SPF standard says not to reject on this alone.?all(neutral): no opinion. Microsoft only suggests it for testing.
Google’s example record ends in ~all. Microsoft recommends -all once you also have DKIM and DMARC.
Never use +all. It lets anyone send email as your domain.
Do I Need a PTR Record?
Your sending server needs one, but you usually won’t create it. The PTR record belongs to whoever owns the sending IP, normally your email provider. Our guide to PTR records explains more.
What Does SPF PermError Mean?
A permerror means a server couldn’t read your SPF record. You need to fix it in your DNS.
The usual causes:
- More than 1 SPF record
- More than 10 DNS lookups
- More than 2 void lookups
- A typo in the record
You may also see a temperror. That’s a short-lived DNS problem that usually clears up. Google Postmaster Tools shows how much of your Gmail traffic passes SPF.
Do I Need to Merge My DKIM Records?
No. Each DKIM record has its own name, called a selector, like mail._domainkey.example.com. So, several DKIM records side by side are normal.
Long DKIM keys are sometimes split into strings inside 1 record. That’s normal too. Here’s how to split a DKIM record.
Next, Check Your DMARC Record
SPF is 1 of 3 email authentication methods. Most providers use it with DKIM and DMARC.
Now that SPF is fixed, see our guide on how to create a DMARC record. It has an example you can copy and paste.
Ready to fix your emails? Get started today with the best WordPress SMTP plugin. If you don’t have the time to fix your emails, you can get full White Glove Setup assistance as an extra purchase, and there’s a 14-day money-back guarantee for all paid plans.
If this article helped you out, please follow us on Facebook and Twitter for more WordPress tips and tutorials.
